 By

Africa’s Digital Future Rests on People, Skills, and Policies
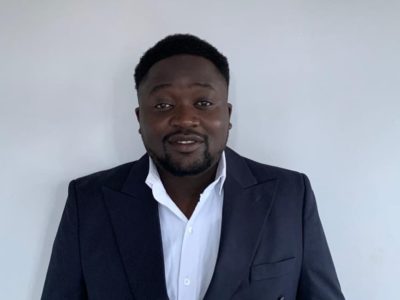
Africa’s digital transformation is accelerating, driven by artificial intelligence, cybersecurity, data-driven innovation and the rapid expansion of digital technologies. But technology alone cannot deliver a secure, ethical and sustainable digital future. The continent’s ability to translate digital investments into lasting economic and social value will increasingly depend on the people, skills, institutions and policies behind the technology. It is against this backdrop that Dr. Abolarinwa Michael Senkoya, Executive Director of the Global Institute for Cyber & Data Security (GICYDAS) and Registrar of the Artificial Intelligence Management & Finance Institute (AIMFIN), Missouri, USA, brings a distinctive perspective to Africa’s emerging digital transformation agenda.
His professional interests sit at the intersection of artificial intelligence, cybersecurity, data protection, technology and responsible digital transformation. For Senkoya, the conversation about Africa’s digital future cannot be separated from the urgent need to build the human capacity required to design, manage, regulate and responsibly deploy emerging technologies. As African governments, businesses and institutions embrace AI and other digital technologies, the continent faces a parallel challenge: developing the professionals, policymakers, regulators and institutions capable of ensuring that digital transformation remains secure, ethical, inclusive and sustainable.
In this interview with IT Edge News.Africa, Ambassador Senkoya examines why human capacity development must advance alongside Africa’s technology ambitions, and why the strength of the continent’s digital future will depend not only on the technologies it adopts, but also on the people and institutions equipped to use them responsibly.
Senkoya Warns of Dangers as Africa Digitises Faster Than It Secures
Give us an overview of GICYDAS; what’s the organisation about?
The Global Institute for Cyber & Data Security (GICYDAS) was established in January 2026 in Missouri, United States of America, as a non-profit educational and professional-development institute focused on cybersecurity, data protection, information security, and responsible digital transformation.
RELATED: Cybersecurity in Africa: Awareness must now become capability
The Institute was established in response to a very important reality: Africa is experiencing rapid digital transformation, but this growth must be accompanied by corresponding growth in cybersecurity awareness, professional competence, and data-protection practices. Our work focuses on education, professional development, research, certification, and capacity building.
We are particularly interested in Africa because the continent is experiencing rapid digital transformation, and we believe Africans should not only be users and consumers of technology, they should also have the knowledge, skills, and institutional capacity to develop, secure, and govern the technologies they increasingly depend upon.
GICYDAS also has a professional presence in Nigeria, with our address at 56 Abudu Oladejo Avenue, Mokore Estate, Warewa, Ogun State.
For us, cybersecurity is not simply an IT issue. It is a matter of leadership, governance, economic security, privacy, and public trust.
Assessing the State of Cybersecurity Awareness Across Africa
What is your appraisal of the state of cybersecurity awareness across Africa?
I would describe the situation as improving, but uneven. Africa has made tremendous progress in digital adoption; we have mobile banking, fintech, digital identity, e-commerce, cloud computing, digital government, and increasingly AI-enabled services. However, cybersecurity awareness has not developed uniformly alongside that growth.
There is often a gap between the speed at which people adopt technology and their understanding of the risks associated with it. The 2026 INTERPOL African Cyberthreat Assessment reported that AI was linked to 55% of reported cybercrimes across Africa. Online scams, ransomware, business email compromise, and digital sextortion remain major threats.
That said, countries like Nigeria are making significant strides. For example, Nigeria has enacted the Cybercrimes (Prohibition and Prevention) Act 2015, which was amended in 2024, and the Nigeria Data Protection Act 2023. These are concrete legislative steps that provide a framework for enforcement and awareness. However, awareness at the grassroots level still lags behind adoption.
We need to move from cybersecurity awareness as an occasional campaign to cybersecurity education as a continuous process. Cybersecurity should not be seen only as the responsibility of an IT department. The board, management, employees, customers, developers, and regulators all have a role. Digital adoption without corresponding digital security awareness creates an expanding attack surface.
“Governments must establish clear and enforceable cybersecurity, cybercrime, and data-protection framework”
What are the responsibilities of governments in promoting cybersecurity?
Governments have a very significant responsibility because cybersecurity has become part of national security and economic development.
First, governments must establish clear and enforceable cybersecurity, cybercrime, and data-protection frameworks. We are seeing this in Nigeria, for instance, with the Cybercrimes Act 2015 (as amended in 2024) and the Nigeria Data Protection Act 2023. These laws are crucial, but they must be fully implemented and enforced.
Second, governments must build institutional capacity, because regulations are only effective when there are competent people and institutions capable of implementing and enforcing them. Third, governments need to protect critical national infrastructure and develop national incident-response capabilities. Fourth, they must invest in human capacity, cybersecurity professionals, digital-forensics experts, and incident responders.
Fifth, they need to promote cybersecurity education from schools through professional and public-sector training. And finally, governments must encourage responsible information sharing between regulators, financial institutions, telecommunications companies, technology providers, and security professionals.
Government has the responsibility to create the environment in which the ecosystem can become secure
Cybersecurity cannot be solved by government alone, but government has the responsibility to create the environment in which the ecosystem can become secure. And importantly, security and privacy should reinforce one another rather than being treated as competing objectives.
At the regional level, bodies like the African Union (AU) and ECOWAS also have critical roles to play. The AU adopted the Malabo Convention on Cyber Security and Personal Data Protection in 2014, which provides a continental framework. ECOWAS has also adopted a Directive on Fighting Cybercrime, which guides member states. These regional instruments are essential for harmonising laws, facilitating cross-border cooperation, and building a unified approach to cybersecurity across Africa.
“Financial services are certainly among the highest-value targets because they combine money, identity, and highly sensitive personal data”
Which sector of the economy of African countries is most vulnerable to cyberattacks?
I would be careful about identifying one sector as universally the most vulnerable because vulnerability depends on the value of the data, the level of digitalisation, the criticality of the infrastructure, and the maturity of security controls.
However, financial services are certainly among the highest-value targets because they combine money, identity, and highly sensitive personal data, this includes commercial banks, fintech companies, mobile-money platforms, and payment processors. Healthcare is another major concern because it holds extremely sensitive personal information and increasingly depends on digital systems. Telecommunications, government infrastructure, energy, and other critical infrastructure are also attractive targets because disruption can have consequences far beyond a single organisation.
So instead of asking only which sector is “most vulnerable,” I believe we should identify which systems contain the most sensitive information and which systems would cause the greatest societal damage if compromised.
Organisations should adopt cybersecurity by design, conduct regular vulnerability assessments and penetration testing, practice data minimisation, and develop threat intelligence capabilities”
What strategies can be deployed in mitigating these risks?
I think organisations need to move from a prevention-only mentality to a full cyber-resilience model. This means strong identity management, secure architecture, encryption, access controls, and employee awareness. It means continuous monitoring, behavioural analytics, and real-time identification of unusual activity. It means having a tested incident-response plan. And it means maintaining secure backups, business continuity, and disaster-recovery capabilities.
Beyond that, organisations should adopt cybersecurity by design, conduct regular vulnerability assessments and penetration testing, practice data minimisation, and develop threat intelligence capabilities. African countries also need stronger regional cooperation in cybercrime investigation, digital forensics, and intelligence sharing. This is where frameworks like the AU’s Malabo Convention and ECOWAS’s cybercrime directive become very important, they provide a basis for that cooperation.
The key principle is simple: a system is not truly secure simply because it has never been attacked. We should ask how quickly it can detect, contain, and recover from an attack. Prevention is cheaper than recovery.
“AI is becoming both a defensive capability and an offensive capability…. AI is effectively accelerating the cybersecurity arms race”
What’s the role of AI in cybersecurity?
AI is becoming both a defensive capability and an offensive capability. On the defensive side, AI can analyse enormous volumes of activity, identify unusual behaviour, detect fraud, support threat intelligence, and help security teams respond more quickly. But the same technology can be used by criminals to automate phishing, impersonation, social engineering, and other malicious activities.
So we are entering a situation where AI is effectively accelerating the cybersecurity arms race. The answer is not to fear AI. The answer is to develop responsible AI governance, stronger human oversight, and security systems capable of adapting to AI-enabled threats. We need human-supervised AI cybersecurity systems because cybersecurity decisions can have serious legal, financial, and human consequences.
AI will not eliminate cybercrime; it will change the speed, scale, and sophistication of both attack and defence. Responsible AI must incorporate security, privacy, accountability, transparency, and appropriate human oversight.
Privacy should also be considered at the design stage of new products and services
What can you say about privacy compliance by companies in Africa?
There has been considerable progress, but compliance remains uneven. African countries have increasingly developed data-protection and privacy laws. The challenge is that having a law is not the same as achieving compliance.
One important problem is that some organisations still treat privacy as a document or legal requirement rather than as an organisational practice. Having a privacy policy on a website is not the same thing as having effective privacy governance. Organisations need to know what personal data they collect, why they collect it, where it is stored, who has access to it, who they share it with, how long they retain it, and what happens when there is a breach.
Privacy should also be considered at the design stage of new products and services, rather than after the system has already been deployed. This is particularly important with artificial intelligence because AI systems can process large volumes of personal information and generate new inferences about individuals from seemingly ordinary data. Privacy should become part of corporate governance and enterprise risk management.
Every citizen should develop basic digital-security habits
Why should the average citizen care about data protection?
Because your data is part of your identity. Your name, phone number, financial information, health information, location, photographs, biometric information, and online behaviour can all tell someone a great deal about you. If that information falls into the wrong hands, it can be used for fraud, identity theft, blackmail, discrimination, impersonation, or other forms of harm.
So data protection is not an issue reserved for lawyers, IT professionals, or regulators. It is about protecting the ordinary person’s identity, dignity, finances, and freedom. When people say “I have nothing to hide,” I usually remind them that privacy is not about hiding wrongdoing. It is about maintaining control over information about yourself.
Every citizen should develop basic digital-security habits: use strong and unique passwords, enable multi-factor authentication, avoid suspicious links, verify financial requests, and limit unnecessary sharing of personal information. The ordinary citizen is not outside the cybersecurity system, every citizen is part of the cybersecurity ecosystem.
Data residency is important, but sovereignty goes beyond physical location
How do we guarantee data protection and residency in Africa amidst the dominance of hyperscalers?
I don’t think the answer is to reject hyperscalers. Cloud computing is already an important part of Africa’s digital development. The issue is governance and strategic control.
African organisations need to know where sensitive data is stored, where it is processed, who can access it, what legal jurisdictions apply, and what happens if the relationship with a cloud provider changes. For sensitive and strategically important data, organisations should apply appropriate data-classification policies, encryption, strong access controls, contractual safeguards, and clear data-residency requirements.
Africa also needs greater investment in trusted regional cloud infrastructure…and interoperable regulatory framework
At the national and continental level, Africa also needs greater investment in trusted regional cloud infrastructure, data centres, digital infrastructure, and interoperable regulatory frameworks. And we need African cybersecurity and cloud expertise, true digital sovereignty requires people who understand cloud architecture, cybersecurity, privacy engineering, and data governance.
Data residency is important, but sovereignty goes beyond physical location. A server being physically located in Africa does not automatically mean the data is sovereign. Data residency is about where data is. Data sovereignty is about who has legal and practical control over it. Africa should participate fully in the global digital economy while maintaining meaningful control, security, and accountability over strategically important data.

Abolarinwa Michael Senkoya, Executive Director, GICYDAS Africa may digitise faster than it secures. Digital transformation is essential to Africa’s economic future, but digital transformation without cybersecurity creates digital vulnerability
What’s the best way for African countries to pursue digital transformation and adoption?
My final thought is that Africa should not approach cybersecurity only from a defensive position. We need to build our own capacity. Africa has talented young people, researchers, technology professionals, and entrepreneurs. We need to invest in their skills and create pathways through which they can contribute to cybersecurity, data protection, AI, and digital transformation.
My greatest concern is that Africa may digitise faster than it secures. Digital transformation is essential to Africa’s economic future, but digital transformation without cybersecurity creates digital vulnerability. We cannot build a trusted digital economy if citizens are afraid to use online banking. We cannot responsibly deploy artificial intelligence if organizations do not understand how to protect the data that AI systems use.
Cybersecurity is not only about preventing attacks. It is also about building trust in the digital economy. And that is one of the reasons GICYDAS exists: to contribute to education, professional development, research, and responsible digital practice.
If Africa wants to participate meaningfully in the next generation of digital transformation, cybersecurity and data protection cannot be treated as afterthoughts. They have to be built into the foundation. Africa’s digital future must be secure, trusted, and responsible.